It is required that planning is signed off before the Completion menu is made available. However, the planning and completion of auditing can take a more iterative approach. For example, you may decide that you are going to place a certain level of reliance on controls and plan your procedures accordingly. When you carry out the field work you may discover that the results of the work do not justify the level of reliance taken and that you therefore need to reduce the level of reliance, which will increase the audit risk required to be covered by substantive work. This will therefore require that you either increase reliance on non-sampling and perform extra work in that area, or accept a higher level of risk to be covered by sampling and increase the work here. In addition, you may identify further Audit Risks during completion and you will wish to enter these and possibly design appropriate procedures in respect thereof.

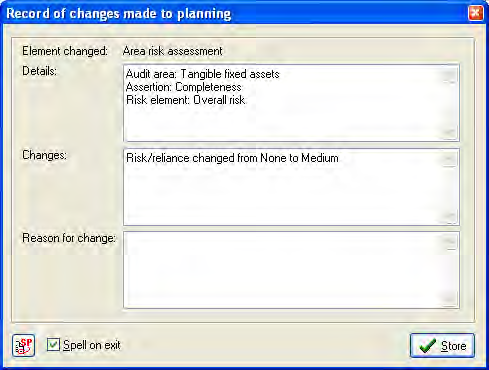
To record the above, you will revisit the area risk routines, which are always available from the main toolbar to give easier access during completion, and change the levels of risk, reliance and planned procedures. The system maintains a log of all changes made to planning following sign off and whenever you make such a change, the system will display the Record of changes dialog showing details of the element changed, the change made and you will be required to enter the reason why you have made the changes.
clipboard_e078c008850ee2e50af5fa61604812a11.png

Enter the reason and click [OK].

You can review all changes made to planning after sign off by selecting the last item from the planning menu. This results in the display of a list of all changes made, from which you can restrict the list to changes made by an individual member of staff and produce a hard copy of the details displayed. list has also been added as the first item on the Review completion dialog.

Related documents

Inherent Risk Questions
This document outlines the process for assessing inherent risk in clients through a systematic approach of questions. The system can store up to 99 risk areas, each containing 99 questions, which are assigned point scores for "Yes" and "No" answers. It details steps for editing, adding, and deleting risk areas and questions, including interface navigation and confirmation prompts. Additionally, it emphasizes that once numbers are assigned to risk areas or questions, they cannot be changed. The document serves as a guide for managing inherent risk assessments effectively.
Audit Risks
This document details the functionality of CCH Audit Automation for recording Identified Audit Risks, also referred to as Significant Business Risks. It provides instructions for users to add, edit, and manage risks, including features for maintaining risks for future audits, assessing their significance, and linking them to assertions. The system includes tools for risk assessment, audit response, and documenting conclusions. Other functionalities encompass risk summarization, printing options, and risk linkage across multiple sources, enhancing the audit process's efficiency and accountability.
Default Specific Risk Questions
CCH Audit Automation allows users to define specific risk questions for audit areas, although it's not mandatory. If no specific questions are set, default questions will be used. Users can edit the default questions through the "Specific risk questions" option in the Risk Model section. Up to 99 default questions can be defined, similar to inherent risk questions. The system utilizes a lookup table that combines specific and inherent risks for audits, with editing instructions provided in the manual.
Risk/Sample Selection
This document outlines the concept of audit risk, defined as the likelihood of undetected material errors during an audit. It introduces a risk model used in Audit Automation that requires total audit risk to remain below acceptable levels across various audit areas. The risks are broken down into inherent risk, control risk, and detection risk, with further subdivisions for detection risk. It emphasizes the importance of understanding these concepts to design effective audit procedures and assess risk at different levels. Additionally, it discusses general and control environments, and the calculation of residual risk, alongside a risk scoring system.
Inherent Risks
The document outlines the procedure for addressing inherent risk questions in an audit context. Users can access a dedicated window to view up to 99 risk areas, answer questions, and modify responses as necessary. The system prompts users to validate changes to ensure proper risk assessments. It includes functionalities for viewing prior comments, copying text, and overriding calculated risk levels, emphasizing that auditor judgment is crucial. Comments on overrides must be provided to rationalize any adjustments made. The document serves as a guide for navigating and utilizing the auditing software effectively.