The authors of master packs can define default identified risks that will apply to all clients that are created and linked to the master. When you create a new client, these risks will automatically appear in the client and will be flagged as risks that should be carried forward on balance forward. Risks defined in master packs will not be added to existing clients.

Once created, the risk can be edited to customise it for the client and audit procedures designed as required. The risk can also be deleted if it is not appropriate to the client. This can be done by any user with a level of senior or above irrespective of the new setting described in Restricting editing of an identified risk to person who raised it.

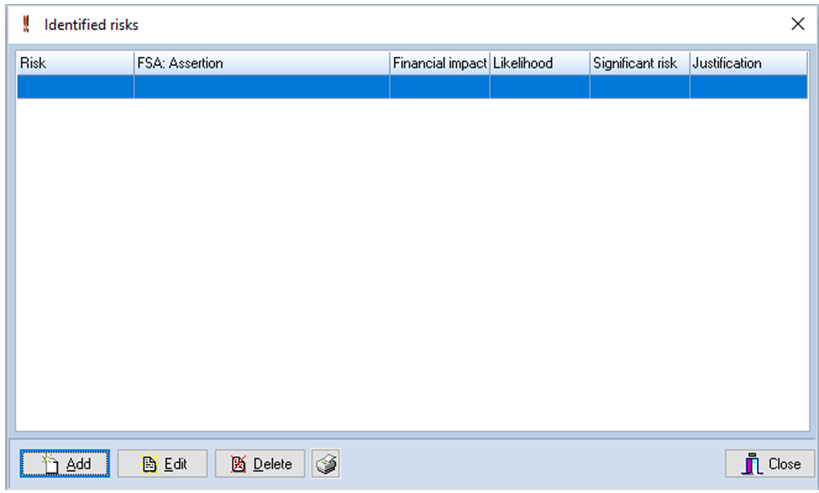
To add, edit or delete default identified risks, load the pack for editing and click on the Default identified risks option with Risk Model in the Master options list.  The system will display the Identified risks dialog.
 

clipboard_e2e4e2ac9d3c3233d53ffa3fd32bcf357.png


Identified risks dialog

Adding a risk

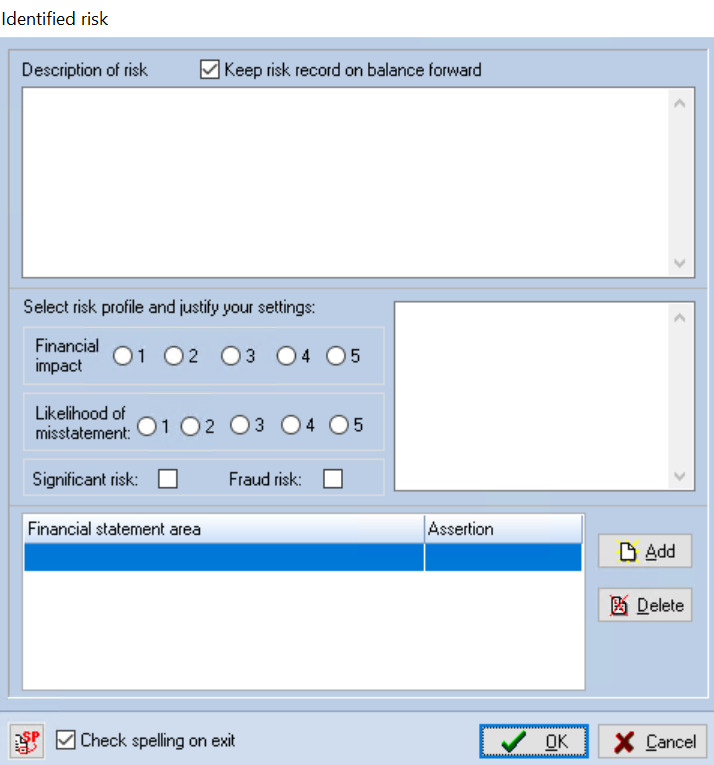
To add a risk, click on the [Add] button.  The Identified risk form will be displayed.
 

clipboard_e513119e4179fc13033df80063bafe5a7.png


Identified risk dialog

  • Description of risk – The description of the risk should be typed in here.
  • Keep risk record on balance forward -  The checkbox is ticked by default to make sure the risk entered and saved here gets balanced forward.  You can uncheck this box if you don’t want it to.
  • Select risk profile and justify your settings 
    • Financial impact – Select the level of significance the risk has
    • Likelihood of misstatement – Indicate the likelihood of the risk materialising

With both of the above levels chosen, use the text box to the right to justify your settings.

  • Significant risk – check this box to indicate a significant risk
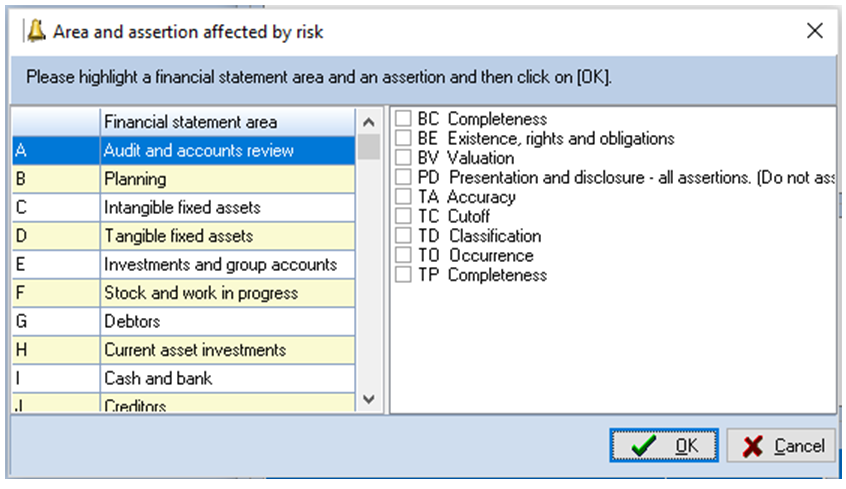
  • Assertions – you can add or delete associated assertions by clicking on the [Add] or [Delete] buttons.  If you choose to add an assertion the following dialog will pop up:
     
clipboard_eed8c23623c5663c3ab7c07fe33350c5e.png

Choose the Financial statement area it relates to from the left-hand side, then check any number of associated assertions from the right and click [OK].  If it relates to more than one area you can then click [Add] again to select another area and choose the related assertions.

Clicking [OK] will then add the new risk to the risk of identified risks

Editing a risk

To edit a risk, highlight it from the list and click on [Edit] or just double click on it and the Identified risk dialog will be displayed for you to edit.  After editing, click on [OK] to save it or [Cancel] to exit the dialog without saving the changes.

Deleting a risk

To delete a risk, highlight it from the list and click on [Delete]. The system will request that you confirm your actions before deleting the entry.

Printing Identified Risks

To print the identified risks, click on the printer icon button.  The system will present the standard Windows printer dialog to allow you to select the printer to use.

Related documents

Inherent Risk Questions
This document outlines the process for assessing inherent risk in clients through a systematic approach of questions. The system can store up to 99 risk areas, each containing 99 questions, which are assigned point scores for "Yes" and "No" answers. It details steps for editing, adding, and deleting risk areas and questions, including interface navigation and confirmation prompts. Additionally, it emphasizes that once numbers are assigned to risk areas or questions, they cannot be changed. The document serves as a guide for managing inherent risk assessments effectively.
Audit Risks
This document details the functionality of CCH Audit Automation for recording Identified Audit Risks, also referred to as Significant Business Risks. It provides instructions for users to add, edit, and manage risks, including features for maintaining risks for future audits, assessing their significance, and linking them to assertions. The system includes tools for risk assessment, audit response, and documenting conclusions. Other functionalities encompass risk summarization, printing options, and risk linkage across multiple sources, enhancing the audit process's efficiency and accountability.
Default Specific Risk Questions
CCH Audit Automation allows users to define specific risk questions for audit areas, although it's not mandatory. If no specific questions are set, default questions will be used. Users can edit the default questions through the "Specific risk questions" option in the Risk Model section. Up to 99 default questions can be defined, similar to inherent risk questions. The system utilizes a lookup table that combines specific and inherent risks for audits, with editing instructions provided in the manual.
Risk/Sample Selection
This document outlines the concept of audit risk, defined as the likelihood of undetected material errors during an audit. It introduces a risk model used in Audit Automation that requires total audit risk to remain below acceptable levels across various audit areas. The risks are broken down into inherent risk, control risk, and detection risk, with further subdivisions for detection risk. It emphasizes the importance of understanding these concepts to design effective audit procedures and assess risk at different levels. Additionally, it discusses general and control environments, and the calculation of residual risk, alongside a risk scoring system.
Inherent Risks
The document outlines the procedure for addressing inherent risk questions in an audit context. Users can access a dedicated window to view up to 99 risk areas, answer questions, and modify responses as necessary. The system prompts users to validate changes to ensure proper risk assessments. It includes functionalities for viewing prior comments, copying text, and overriding calculated risk levels, emphasizing that auditor judgment is crucial. Comments on overrides must be provided to rationalize any adjustments made. The document serves as a guide for navigating and utilizing the auditing software effectively.